/ personal lab / homelab
HomeLab Infrastructure
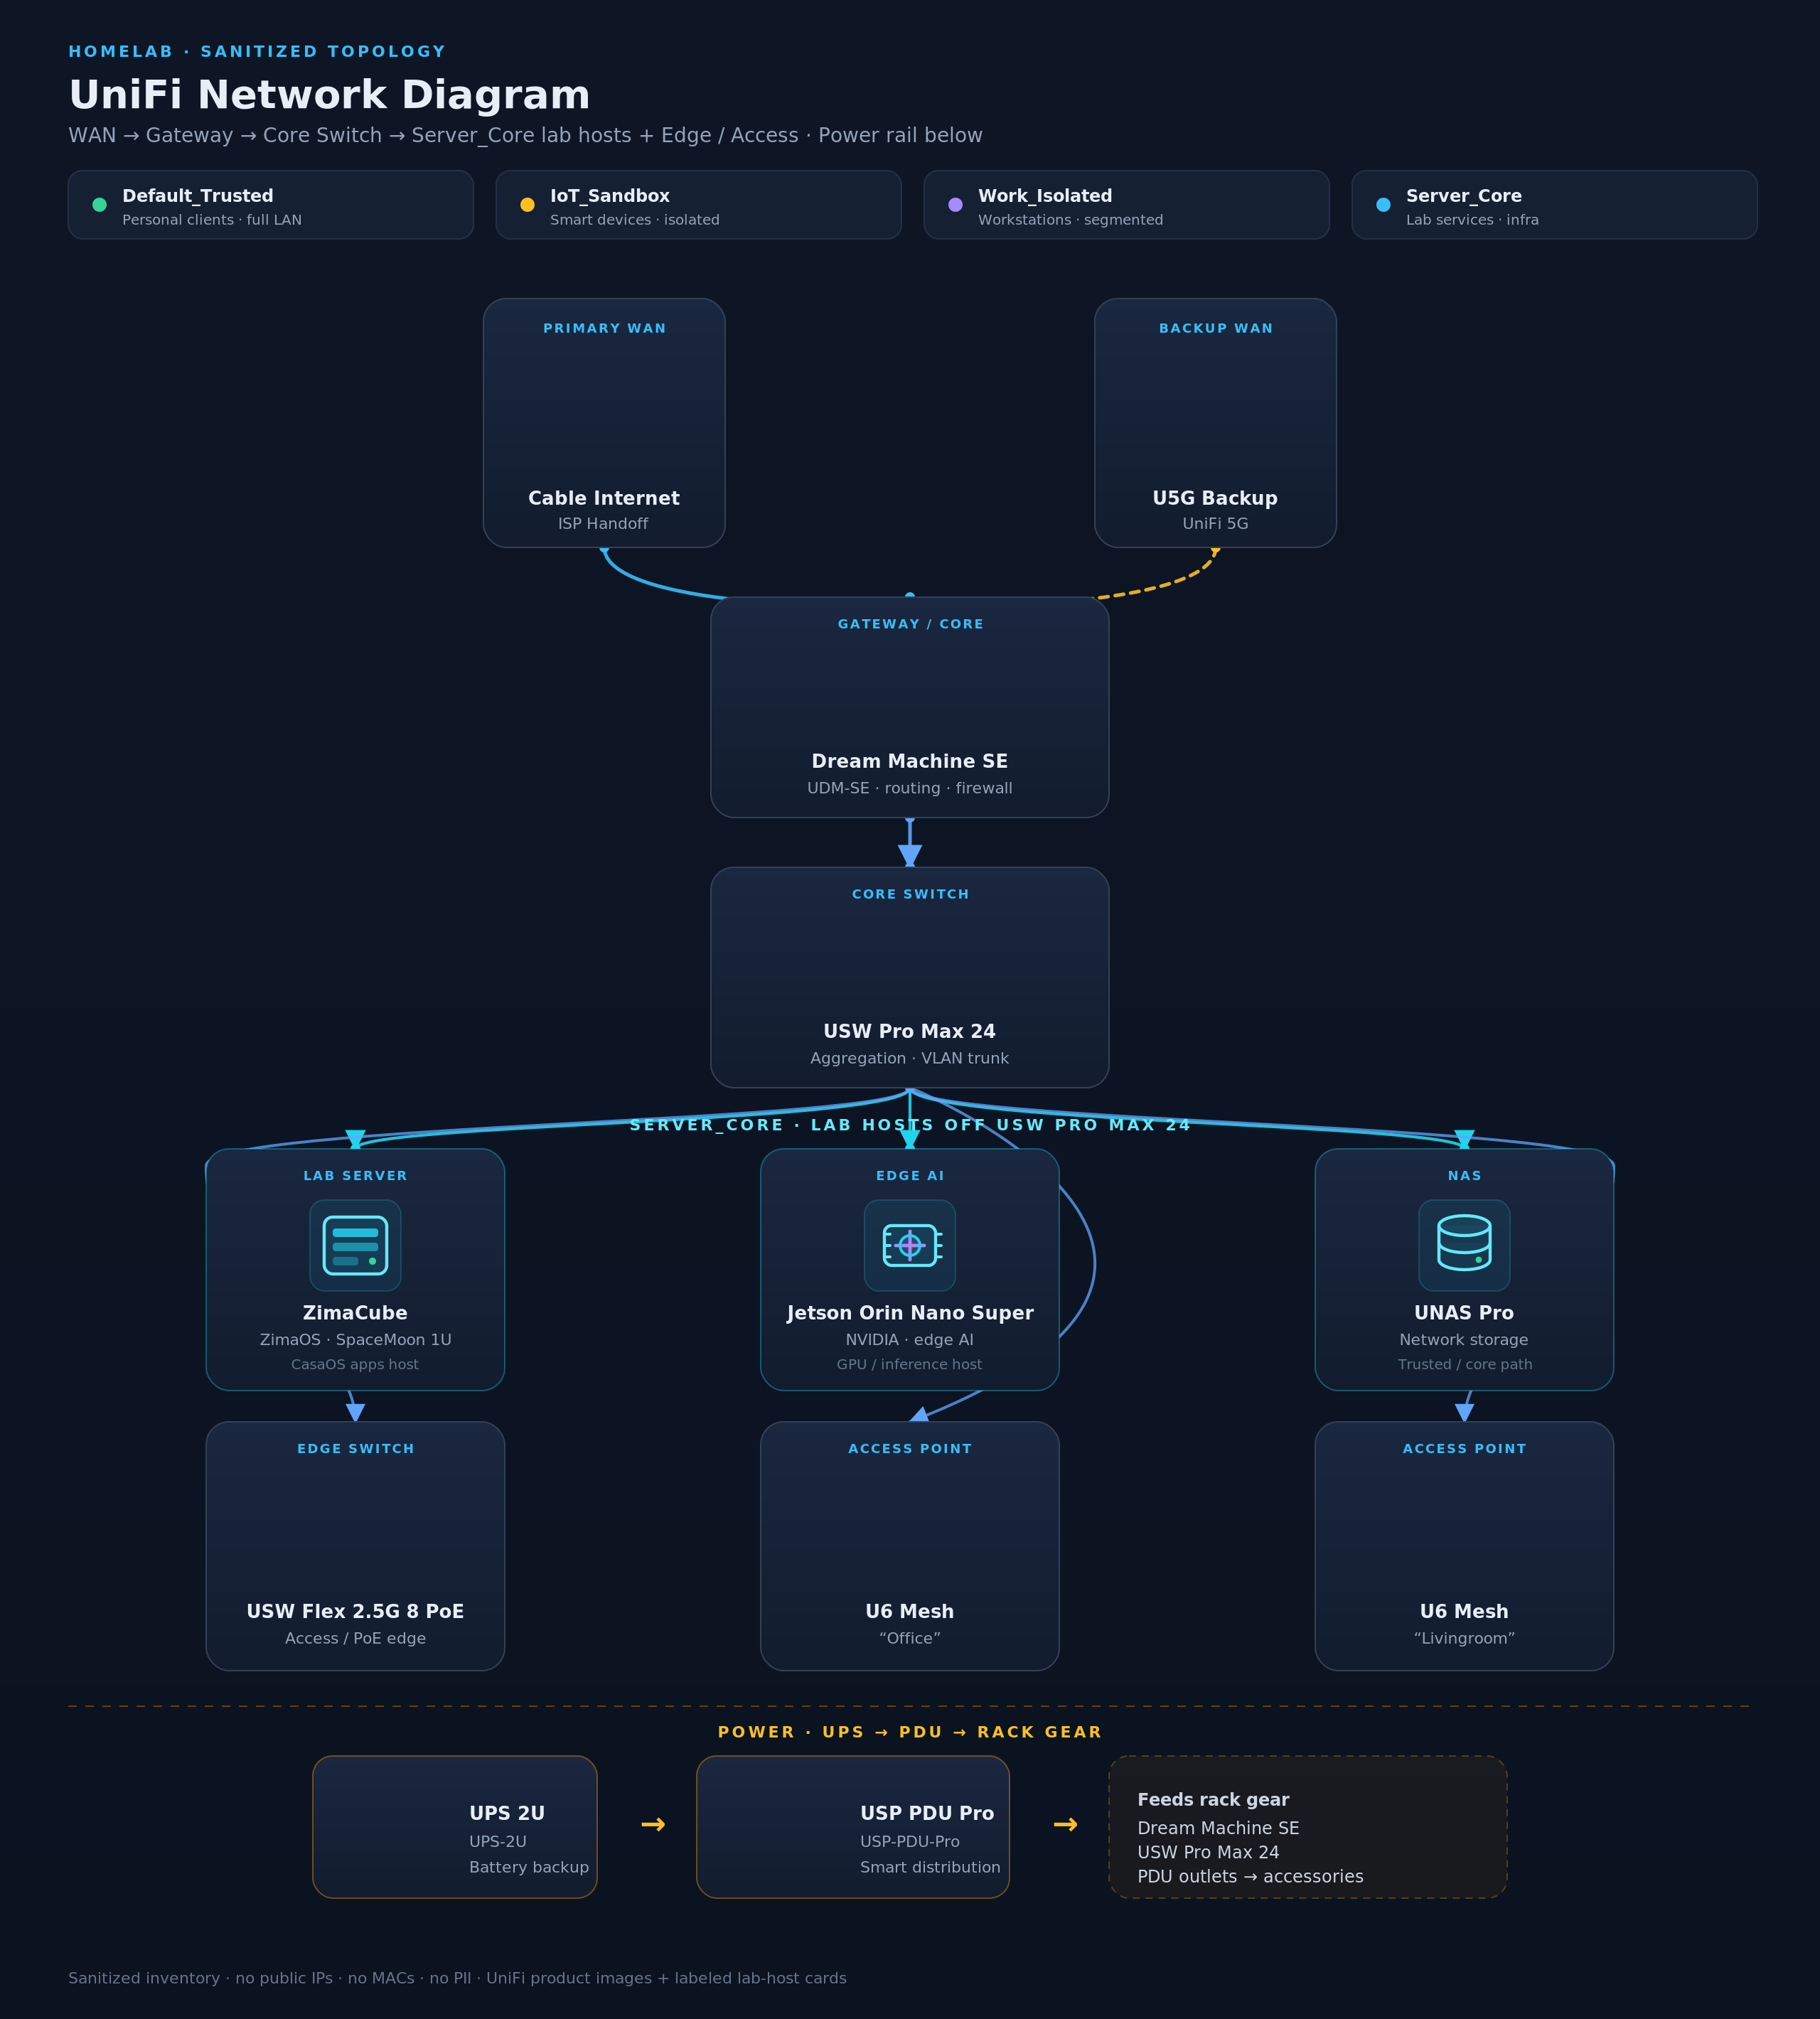
A production-minded home lab built in layers: a UniFi network fabric with separated trust zones, a Server_Core for always-on compute and storage, and a deliberately narrow public edge through Cloudflare Tunnel. ZimaCube runs durable file and service workloads; the Jetson Orin Nano Super owns local AI inference.
Layered design
Each layer has one job, so a failure or change stays inside its layer.
| Layer | Role |
|---|---|
| Edge WAN | Dual WAN: cable primary plus UniFi 5G backup |
| Gateway | Dream Machine SE: firewall, DHCP, VLANs, Wi-Fi, WAN failover |
| Core switch | USW Pro Max 24: VLAN trunks, Flex PoE, U6 Mesh, PDU/UPS, Server_Core |
| Compute | ZimaCube for files and services; Jetson Orin Nano Super for local AI |
| Trust zones | Trusted · IoT · Work · Server_Core VLANs |
| Public surface | Cloudflare Tunnel only — no inbound ports |
Traffic path
- Dual WAN
- Dream Machine SE
- Pro Max 24
- ZimaCube + Jetson
- VLANs + tunnel edge
Internet enters on either WAN, the Dream Machine SE enforces firewall and VLAN policy, the Pro Max 24 trunks zones to access points and Server_Core, and anything public leaves only through Cloudflare Tunnel.